Cross-Account Ingestion
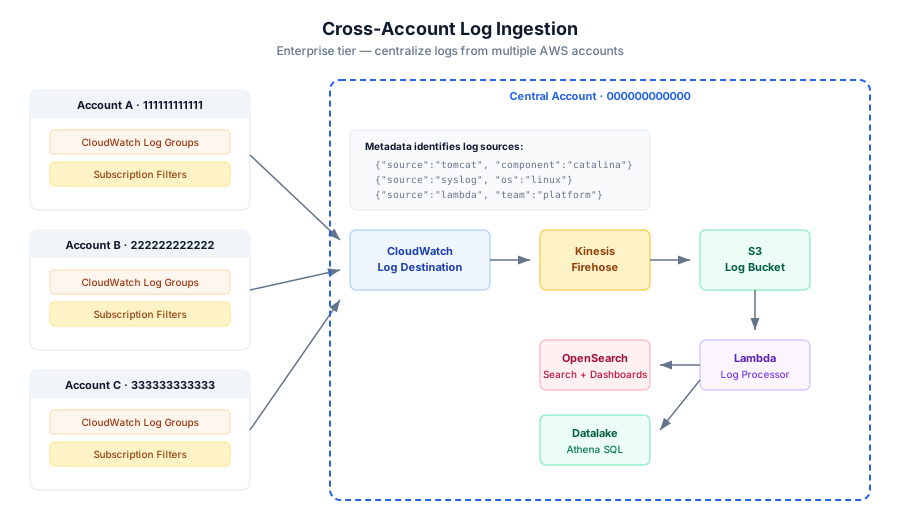
On the Enterprise tier, Log Processor can centralize logs from multiple AWS accounts into a single pipeline. Each account's logs are automatically tagged with the source account ID and are queryable via user-defined metadata in both OpenSearch and Athena, alongside your primary account's logs.
Cross-account log ingestion
Specify an organization ID and/or member account IDs, then set up CloudWatch Logs destinations for cross-account subscription filters from a single editor. Each source account creates a CloudWatch Logs subscription filter pointing to the cross-account destination.
Configuration is set at deployment:
CrossAccountIds— comma-separated AWS account IDs allowed to send logs and replicate S3 access logs to this stack.OrganizationId— if set, any account in the organization can deliver logs without listing individual account IDs.
Cross-account S3 access log ingestion
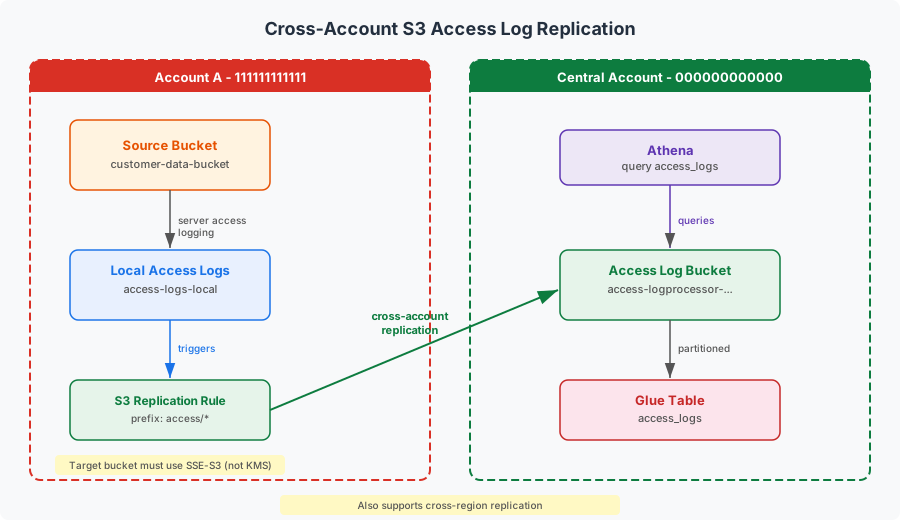
Centralize S3 access logs from multiple AWS accounts into a single pipeline. External accounts replicate their S3 access logs to your stack's access log bucket using S3 replication rules. Use the provided script(s) to configure partitioned access logging, IAM roles, and cross-account replication in minutes. This is cross-region and cross-account capable.
Remote management from the editor
On the Enterprise tier the Subscription Editor supports remote subscription management — browse, subscribe, and unsubscribe log groups in remote accounts in the same region — plus an Accounts management UI to add, remove, and validate remote accounts with one-click role verification. Athena dynamic account discovery automatically detects accounts as logs flow in.