RBAC and Single Sign-On
The subscription editor is secured with Amazon Cognito. Role-based access control and enterprise single sign-on let you control who can view and change monitoring configuration.
Multi-factor authentication
Because sign-in is handled by Amazon Cognito, MFA (TOTP authenticator apps) is available on every tier that includes the Cognito-secured editor — it is not a higher-tier add-on. MFA is user-controlled: enable it or leave it off as you prefer. The enterprise tier adds the option to require MFA for all users (org-wide enforcement); even then, turning it on or off remains your choice.
Role-based access control (RBAC)
Editor roles are available on the advanced tier and above. Assign admin and viewer roles via Cognito groups to separate users who can change configuration from those who can only view it.
Single sign-on (SSO)
SSO is available on the enterprise tier, supporting SAML and OIDC federation with Okta, Azure AD, Google, or any standards-compliant identity provider.
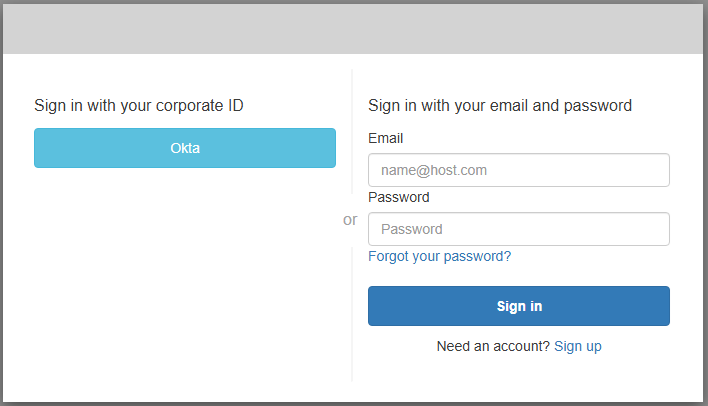
Add your identity provider to the Cognito User Pool using the sso helper script. Users then see a "Sign in with [Provider]" button on the login page. After first login, assign groups with the groups script for role-based access. The helper scripts (.cmd/.sh) are in Guides & Downloads.
A Single Sign-On Integration Guide and a User Management Guide (both PDF) are available in Guides & Downloads.